Sync your .env files and secrets anywhere. One command.
dotvault encrypts your .env files, .npmrc, kubeconfig and other secrets, and hands them to the people, CI jobs and AI agents you allow — with a single dotvault pull. No more pasting .env into chat or a wiki.
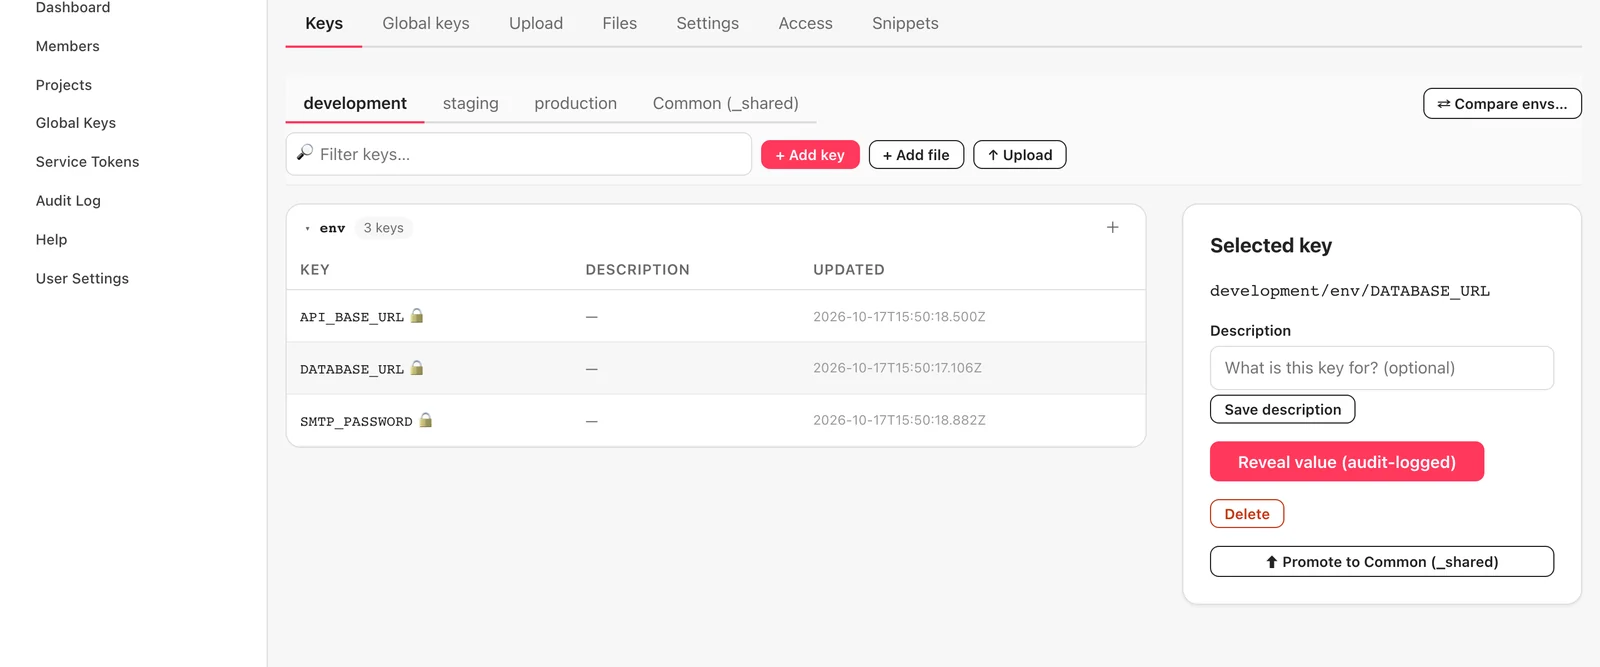
The console and the CLI see the same values
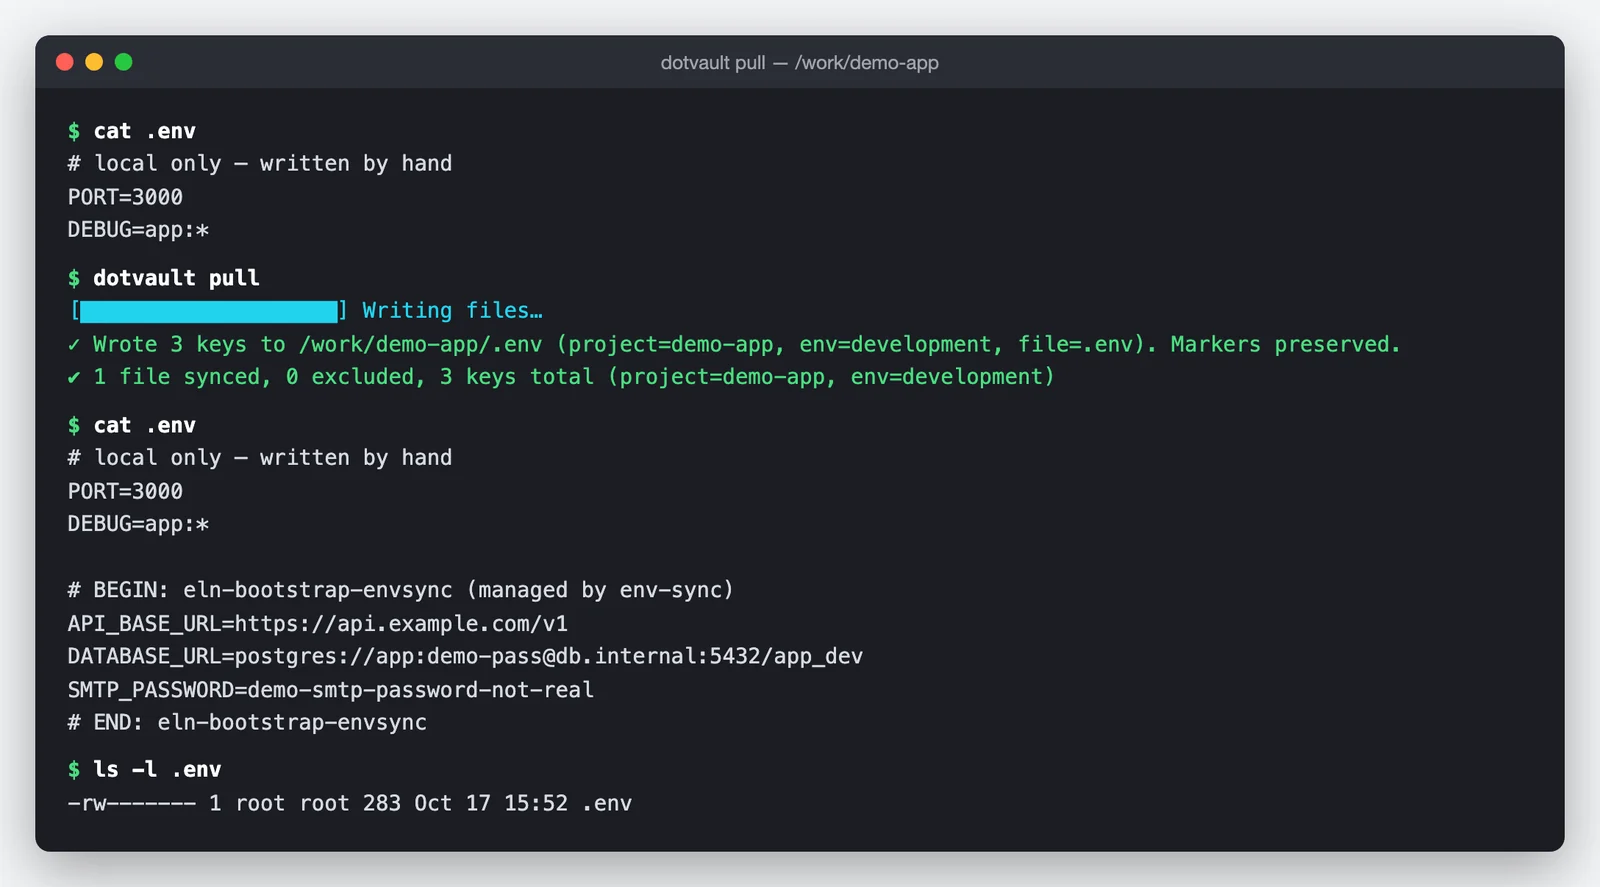
Values you enter in the browser reach your laptop, CI and AI agents through dotvault pull. Lines you wrote by hand stay; only the managed block is rewritten.
Get started in 3 steps
Create an account, log in with the CLI, and pull. New teammates follow the same steps on day one.
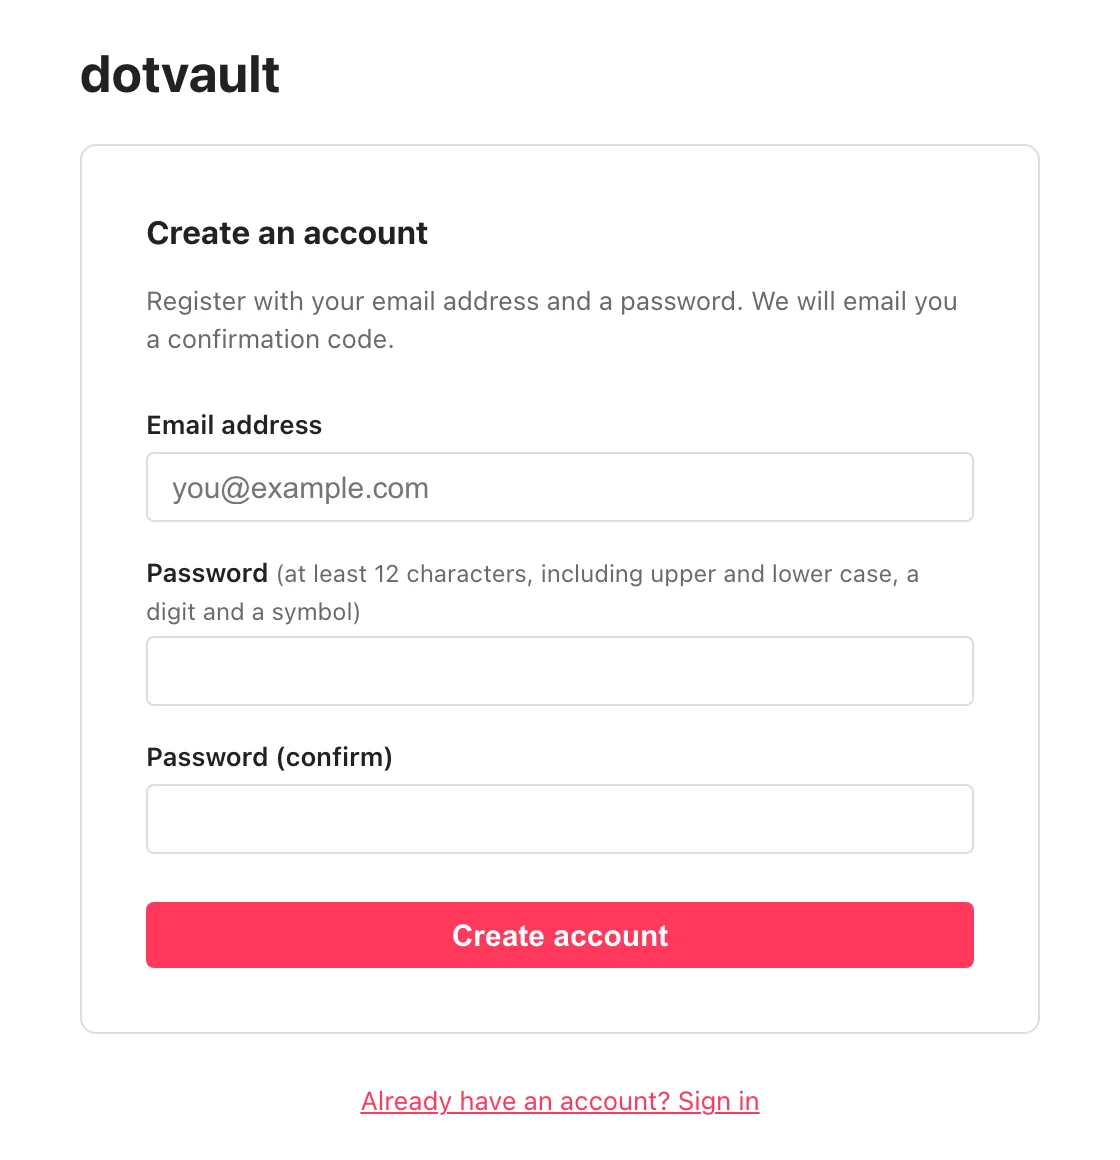
1Create an account
Sign up at app.dotvault.io with an email and a password.
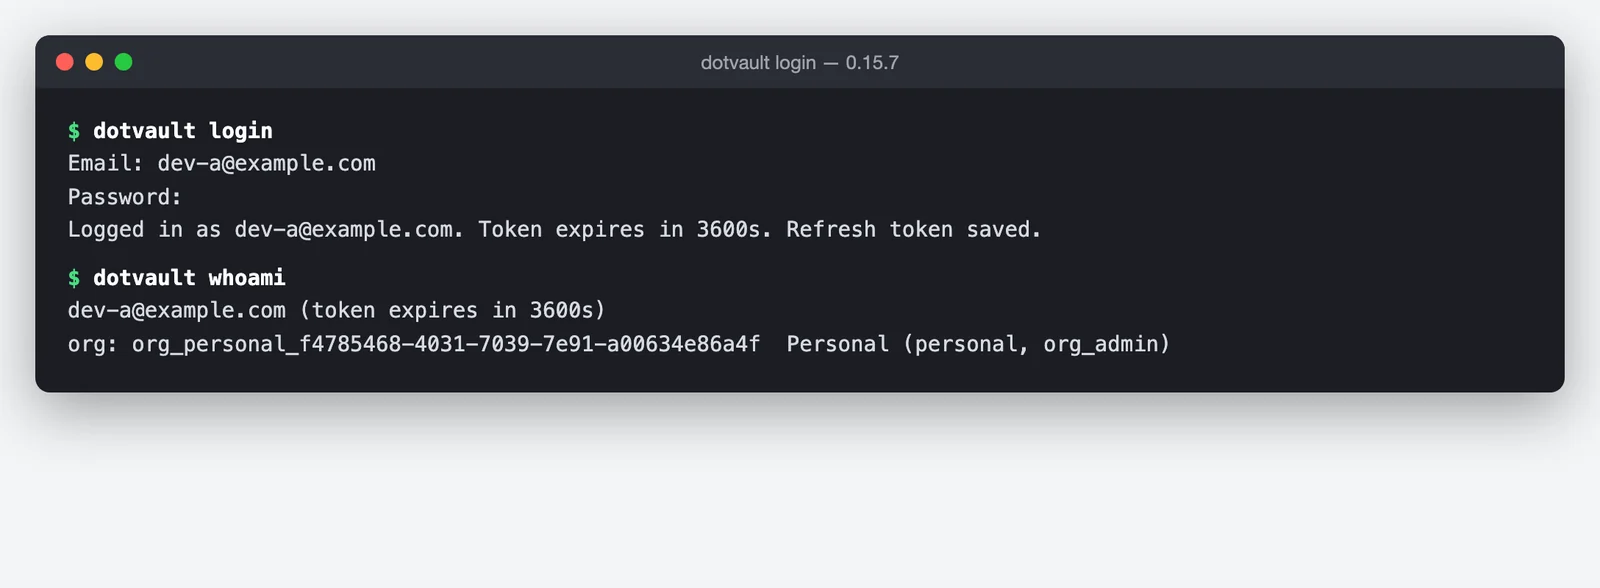
2Log in with the CLI
Install with npm i -g @earthlink/dotvault, then dotvault login.
3Pull
Run dotvault pull in your project folder and your .env is ready.
What you can do
Everything you need to hand out secrets, in one service. Every image below is the real product.
One project for every environment — and see the differences
Keep development, staging and production in one project. Compare two environments side by side and copy a missing key in one click. Put values shared by every environment in Common, so you fix them in one place.
Read the guide →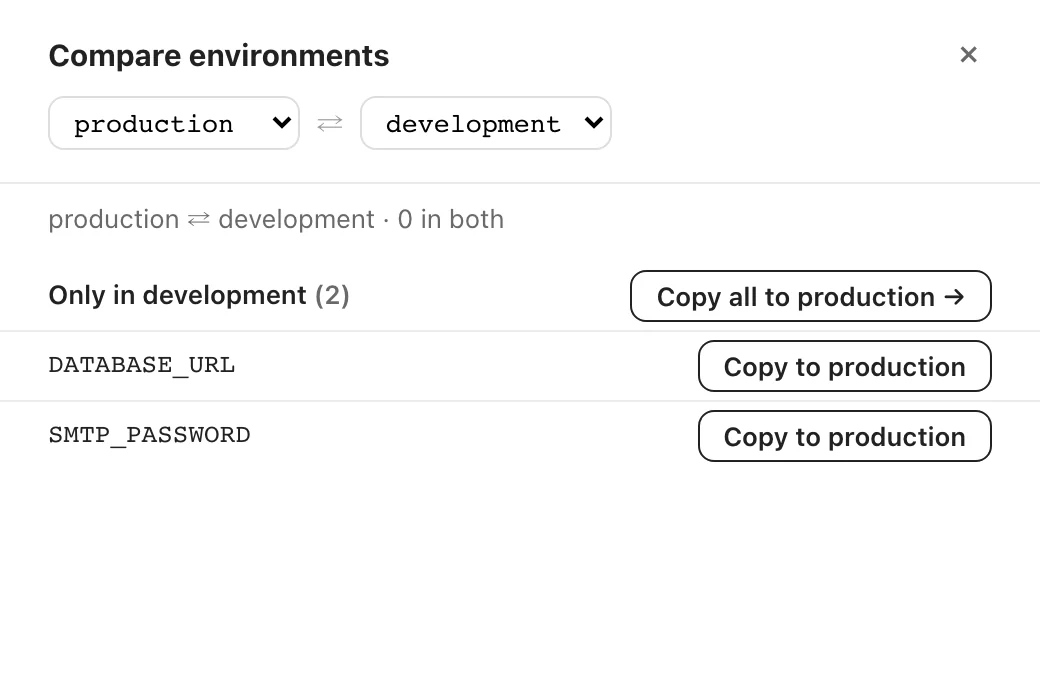
Overwrote a value? Roll it back
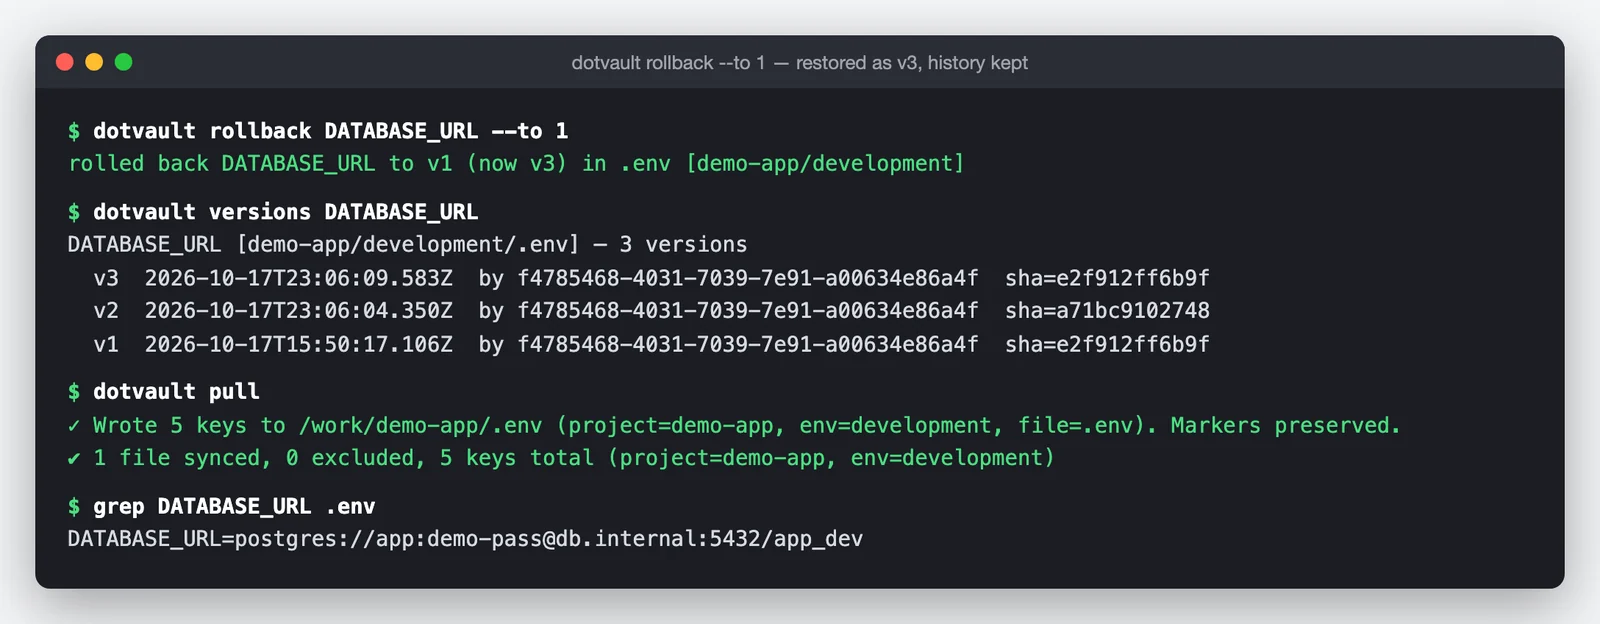
Every key keeps its version history. dotvault versions shows who changed it and when; dotvault rollback --to 1 restores an earlier value — and the rollback itself is kept as a new version.
Ship .npmrc and kubeconfig as whole files
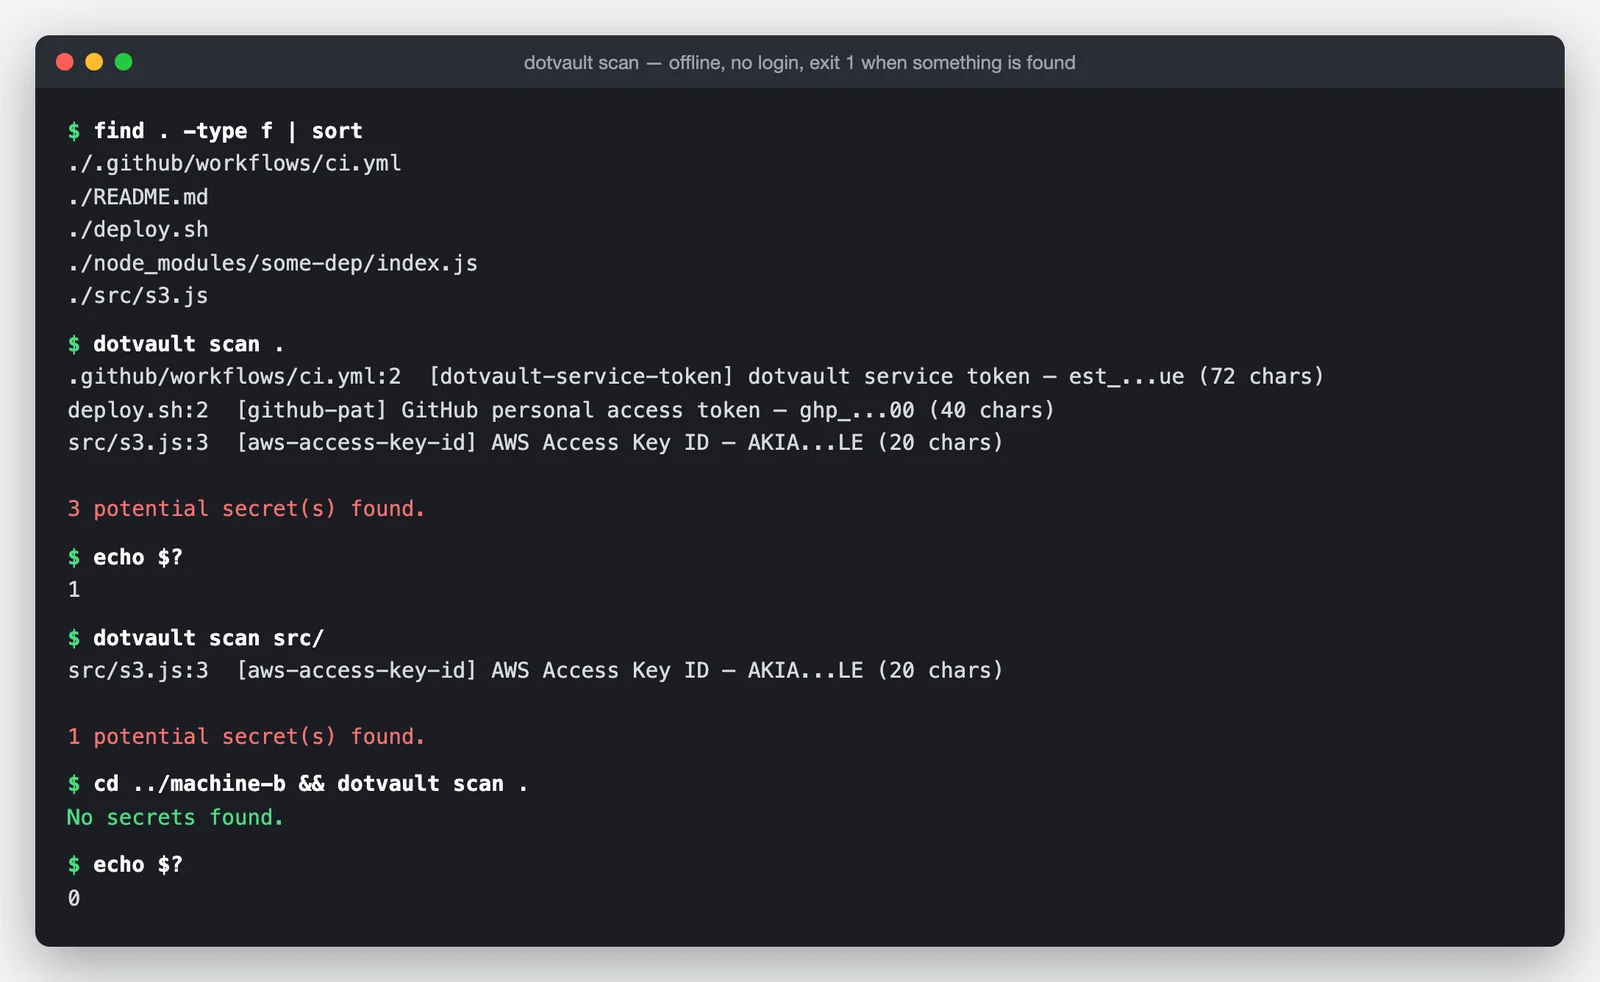
Files that are not key=value pairs go up as-is with dotvault push. Before you commit, dotvault scan finds secrets that slipped into your code — offline.
One place for values every project uses
Keep a Sentry DSN or a Cloudflare token in Global Keys. Only the projects that bind a key receive it, and you can override it per environment.
Read the guide →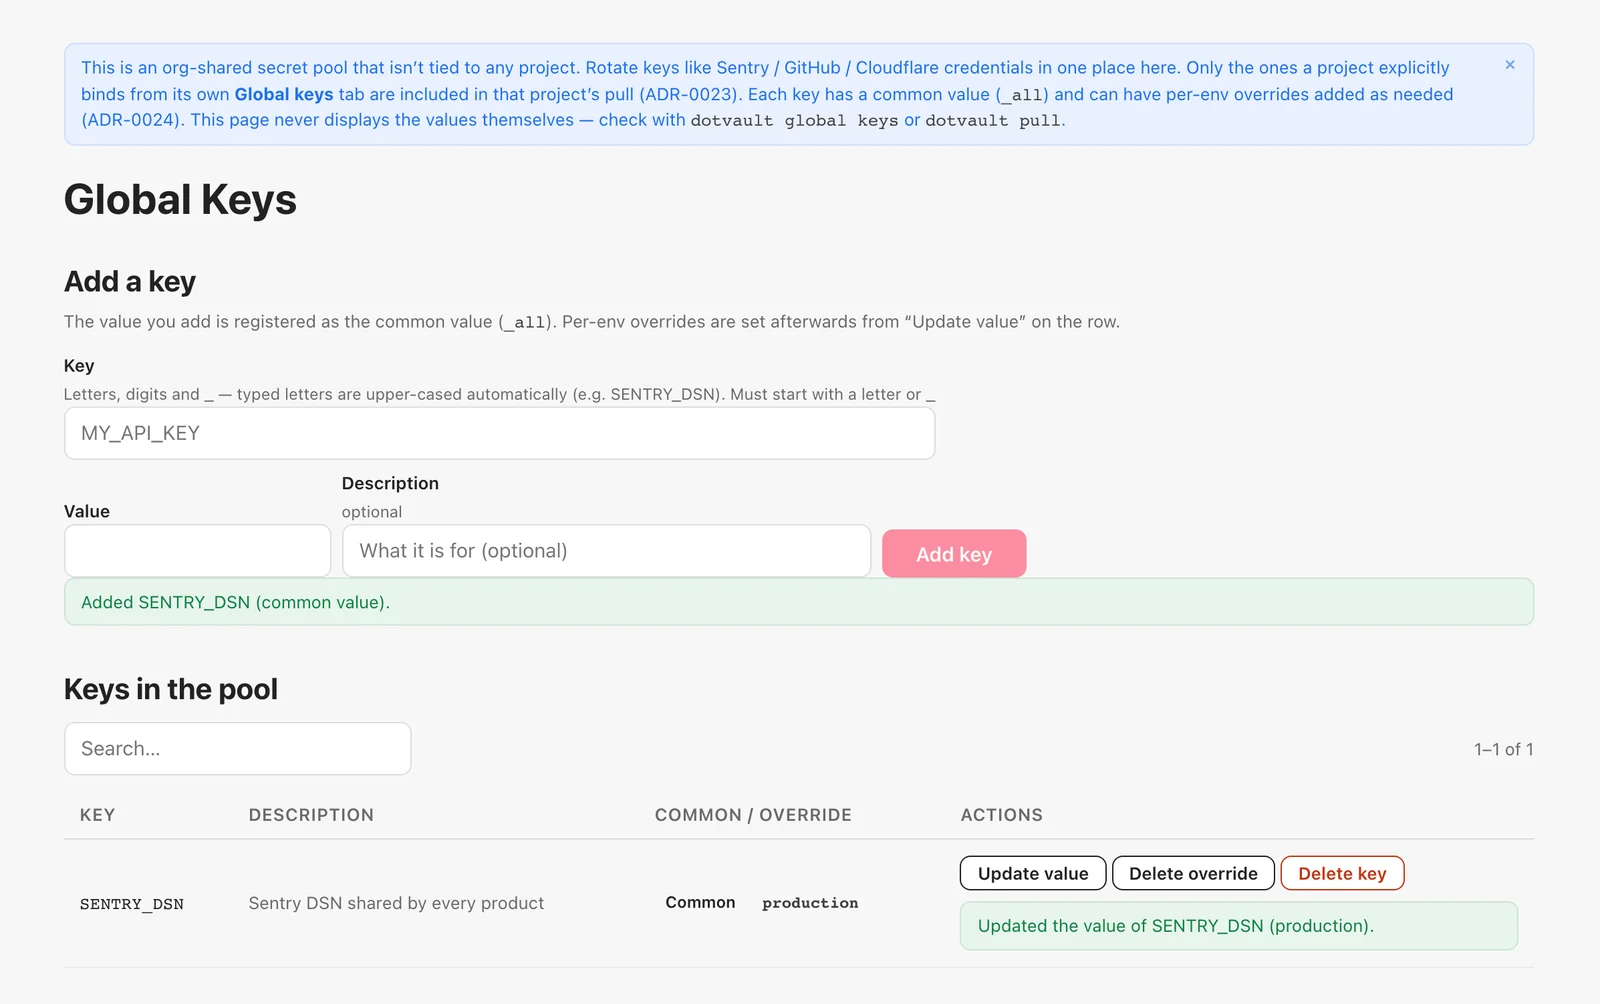
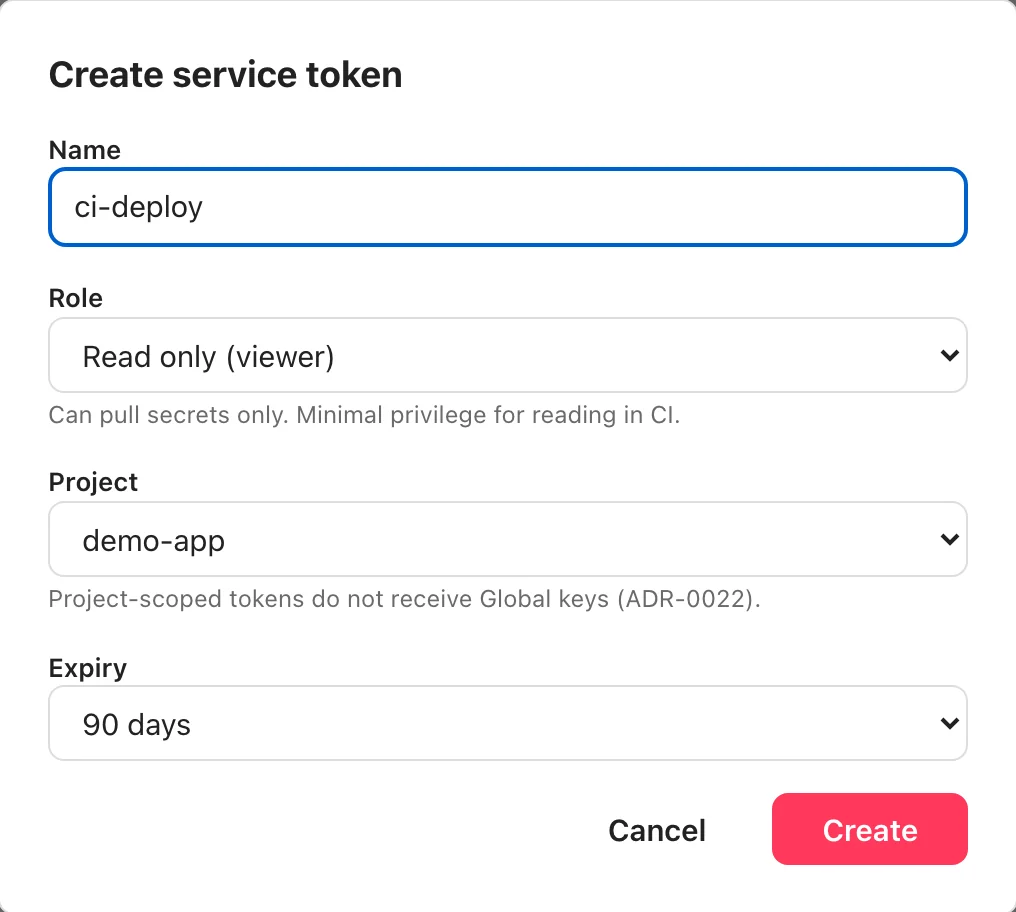
Give CI one short-lived token — not your password
Create a read-only service token scoped to one project that expires in 90 days, and put it in GitHub Actions as DOTVAULT_TOKEN. Revoke it and it stops working immediately.
A scoped token for your AI agent
Instead of pasting .env into Claude Code or another agent, hand it one token limited to a project and an environment. Everything it reads is in the audit log, and you can revoke it any time.
Read the guide →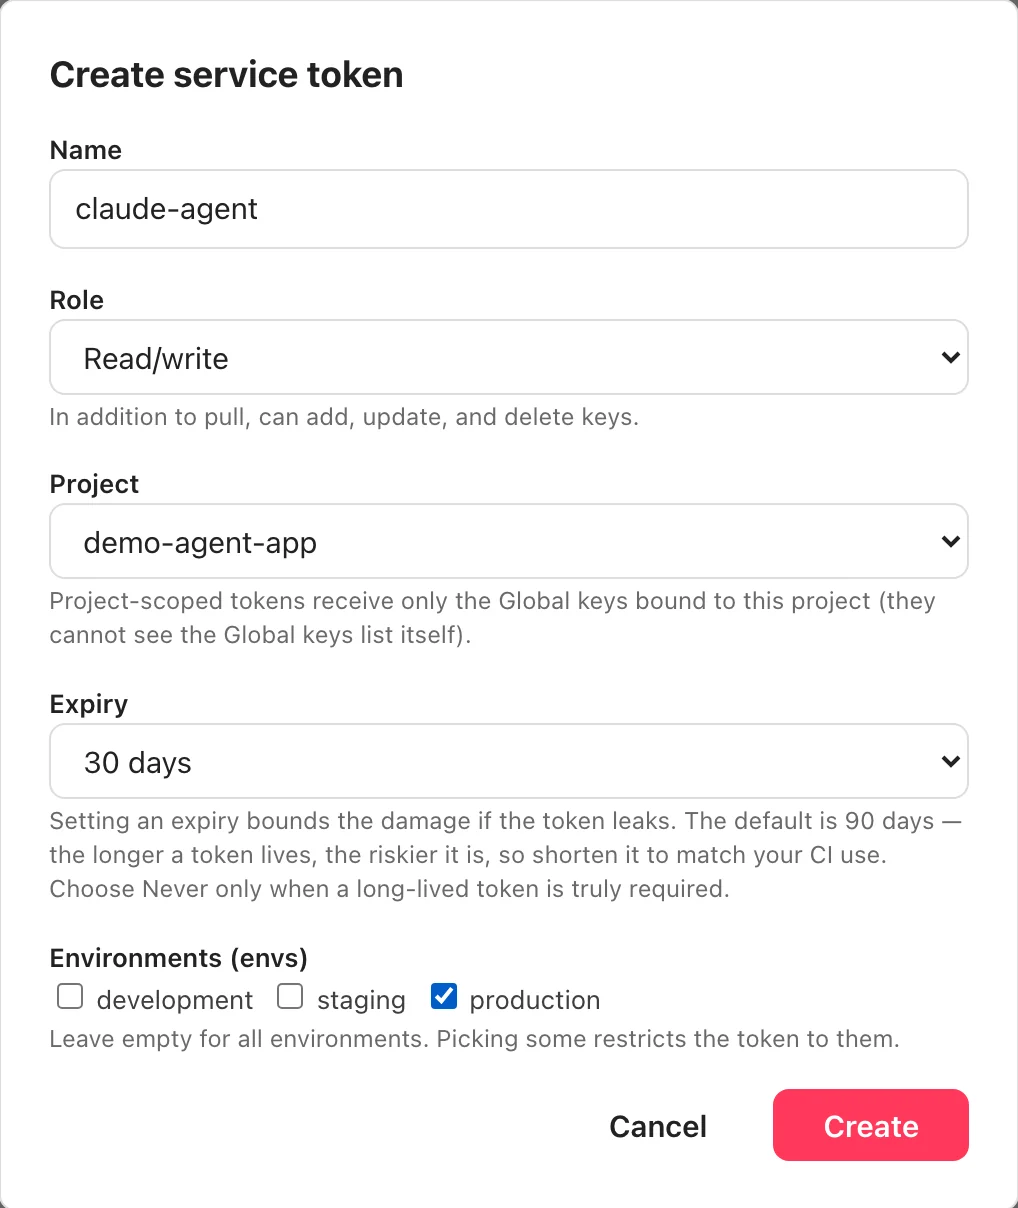
Invite people, scope what they see, shut a leaver out
Invite by email and choose an org role (org_admin, member, guest) and a project role (owner, admin, writer, reader), scoped to the environments you pick. Guests only see the projects you grant. Remove someone and their tokens and grants go with them.
Read the guide →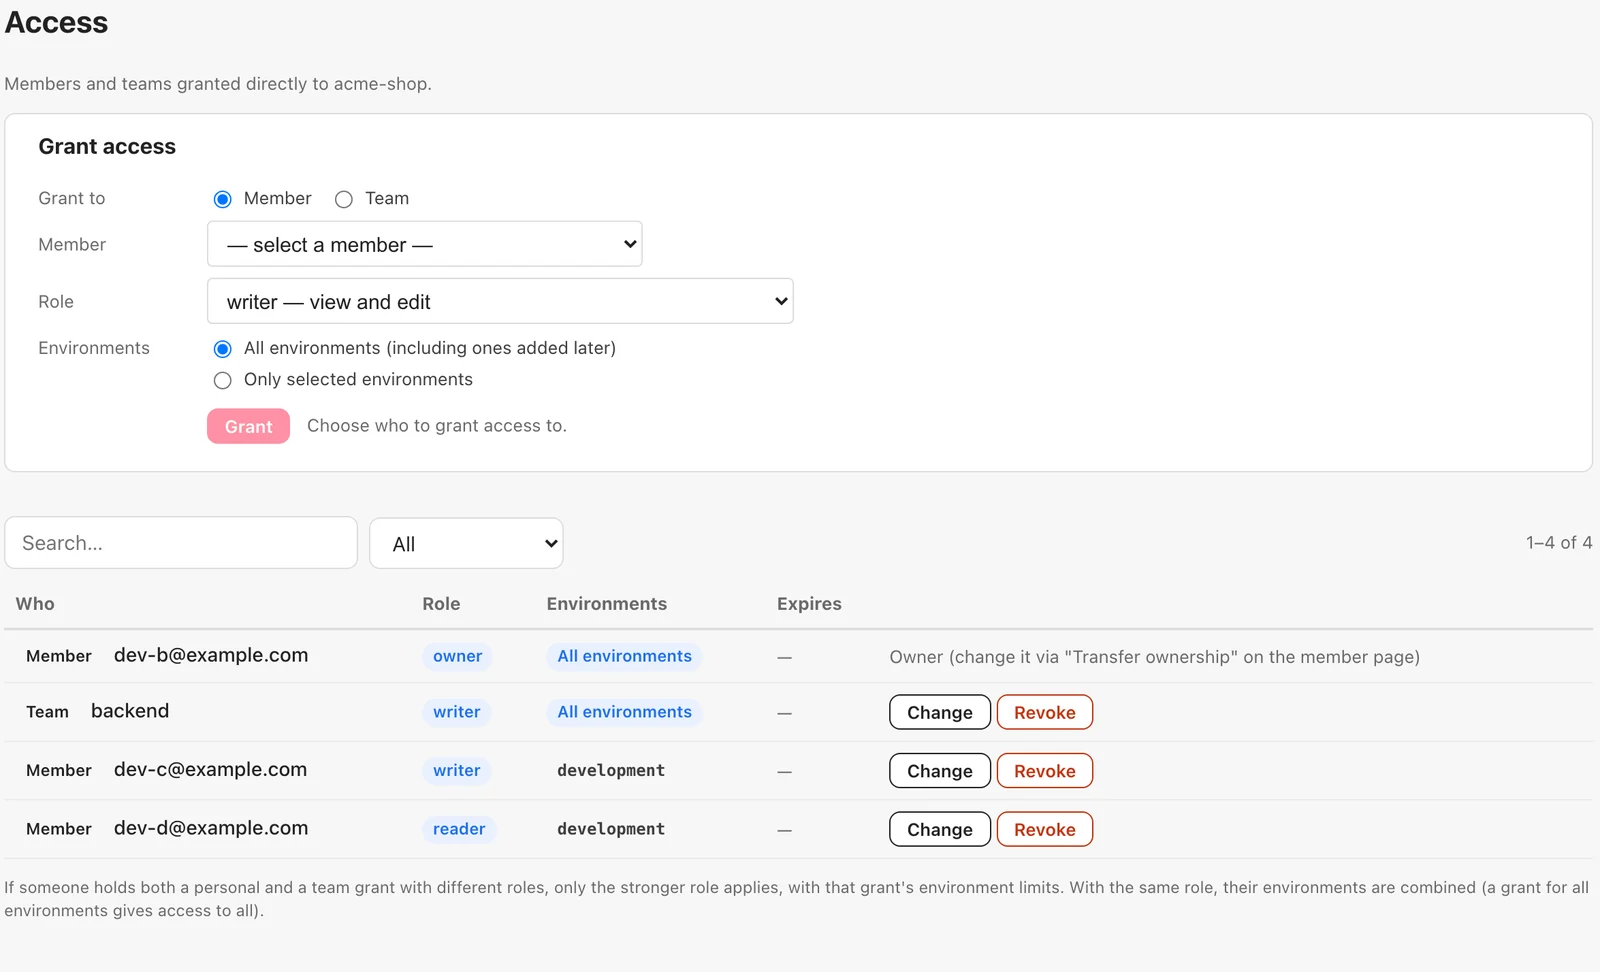
Know who did what, and when
Every reveal, change, token creation and revocation is recorded. Filter by action, actor, target and date.
Read the guide →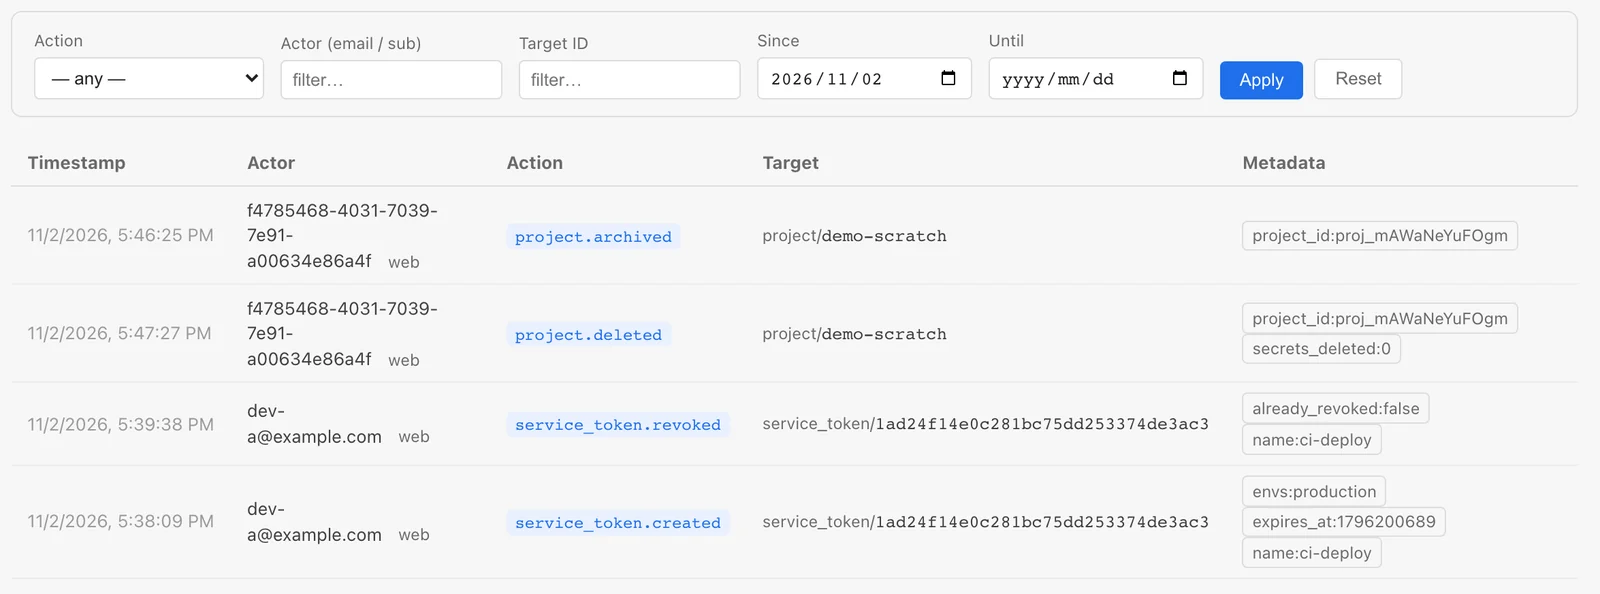
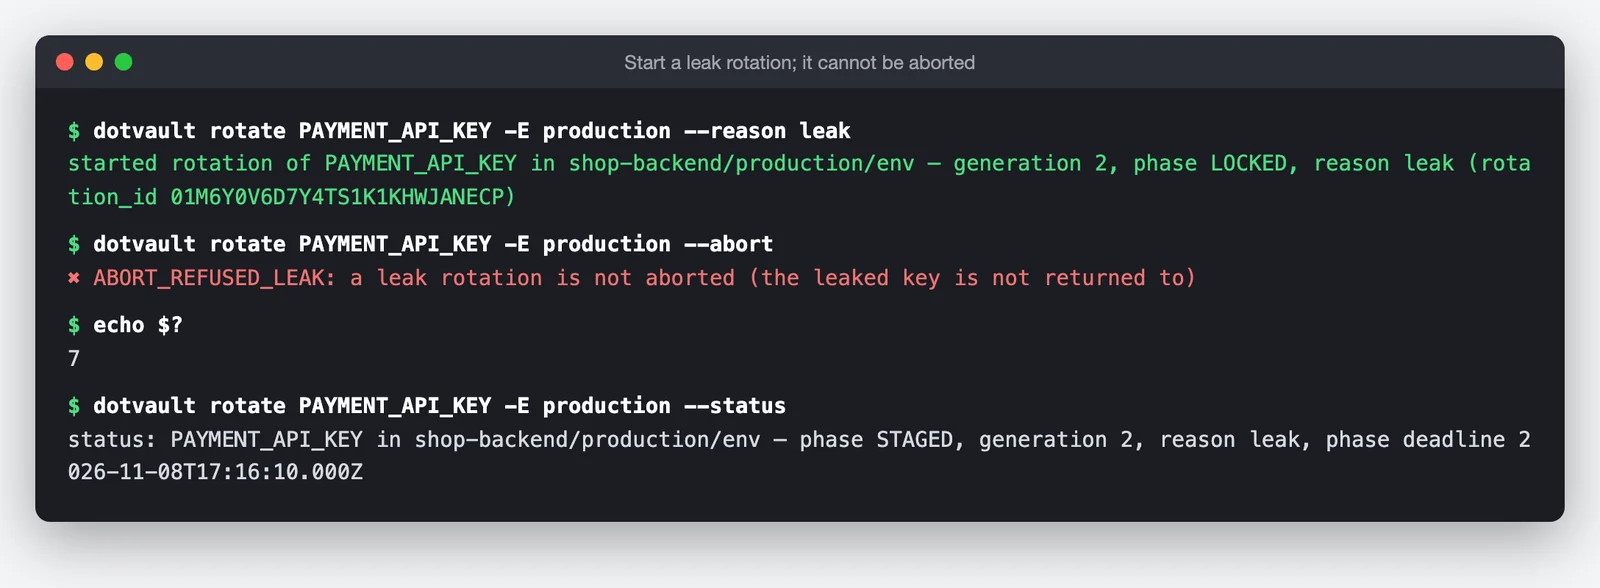
Rotate a leaked key without downtime
dotvault rotate delivers the new value, confirms every consumer has it, and only then revokes the old one. A leak rotation cannot be aborted, so the leaked value never comes back.
Built for these moments
Solo developers
Run dotvault init, login, and pull to keep .env in sync across every machine you code on.
Development teams
Onboarding a new teammate is login + pull — no more sending .env files over Slack.
CI/CD pipelines
Store a service token as DOTVAULT_TOKEN in your CI secrets, then dotvault pull --env production for production secrets.
Organizations running multiple products
Shared credentials like a Cloudflare token live in the global key pool — only the projects that need them bind in.
Teams syncing more than .env
.npmrc, kubeconfig, certificates — dotvault push brings them into the same sync flow.
Pricing
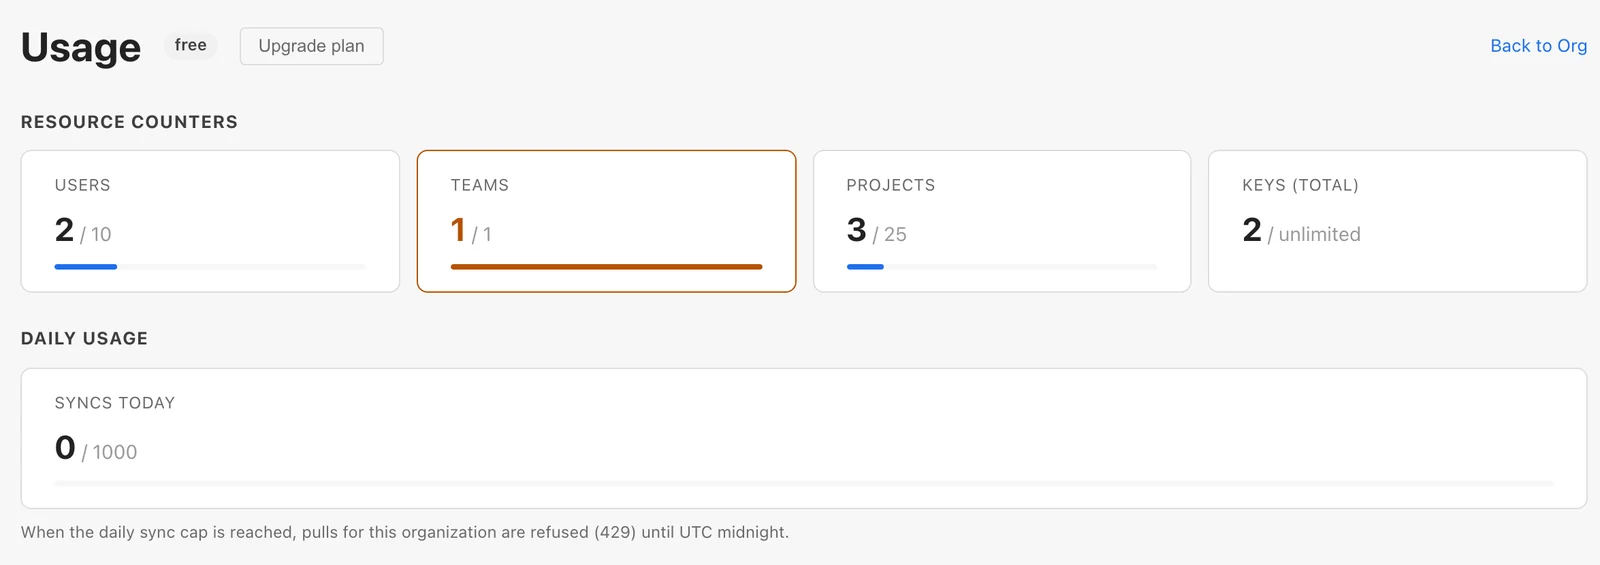
dotvault is free to use. The Usage screen in the console always shows your current usage and limits.
Personal
- Unlimited projects
- Unlimited keys
- Up to 10 environments per project
- 14 days of audit log
Company (free plan)
- Up to 10 members
- Up to 25 projects · 1 team
- Unlimited keys · up to 10 environments per project
- 1,000 pulls per day · 14 days of audit log
Stop pasting .env files into Slack. Secrets shouldn't be copied around — they should be pulled by whoever's authorized. That's dotvault.
Frequently asked questions
Yes. dotvault is published as a free tool for developers. Personal (just you) has unlimited projects and keys. The Company free plan covers 10 members, 25 projects, unlimited keys and 1,000 pulls a day. Both allow up to 10 environments per project and keep 14 days of audit log.
Step-by-step guides
A series that walks through dotvault with real screens and commands.
- 1Sharing environment variables securely with your team: what dotvault is, and where this series takes you
- 2One dotvault pull, the same .env everywhere: laptop, CI, cloud dev environments
- 3Stop editing the same value in every .env: one dotvault project for every environment, one Common layer
- 4Overwrote a secret by mistake? Writing, pulling and rolling back keys
- 5Still sending .npmrc over Slack? Push whole files, scan before you commit
- 6Pasting the same Sentry DSN into every project? Put it in Global Keys once and bind it
- 7Giving CI your own login? Pull secrets into GitHub Actions with one service token
- 8Pasting .env into Claude Code? Give the agent one dotvault service token instead
- 9Invite by email, grant one environment, shut a leaver out in 60 seconds: roles and teams in dotvault
- 10Who revoked that token? Reading the dotvault audit log
- 11Rotate a leaked API key without stopping your services: dotvault hands out the new value first
- 12Day one to
dotvault pullin five minutes
Stop pasting .env. Start pulling it.
Start freeCheck out other products from EarthLink Network.